GrowTrades
VentureOngoing
Founder.
Lead-generation websites with instant quote calculators for local trades businesses. The first client is SCB Handyman Services in Guildford, Surrey.
I started GrowTrades in 2026: a small digital marketing agency that handles the digital side of local trades businesses, so their owners can be more selective about the jobs they take. Each client gets a lead-generation site built to turn local searches into qualified leads, an instant quote wizard that gives customers a price guide and sends the owner the job details, local SEO including their Google Business Profile, automated replies to Google reviews that we approve, analytics that compare before and during the service, and an automated lead flow, with support around the clock. Inside the agency, AI agents automate the work, so onboarding is the only regular manual upkeep.
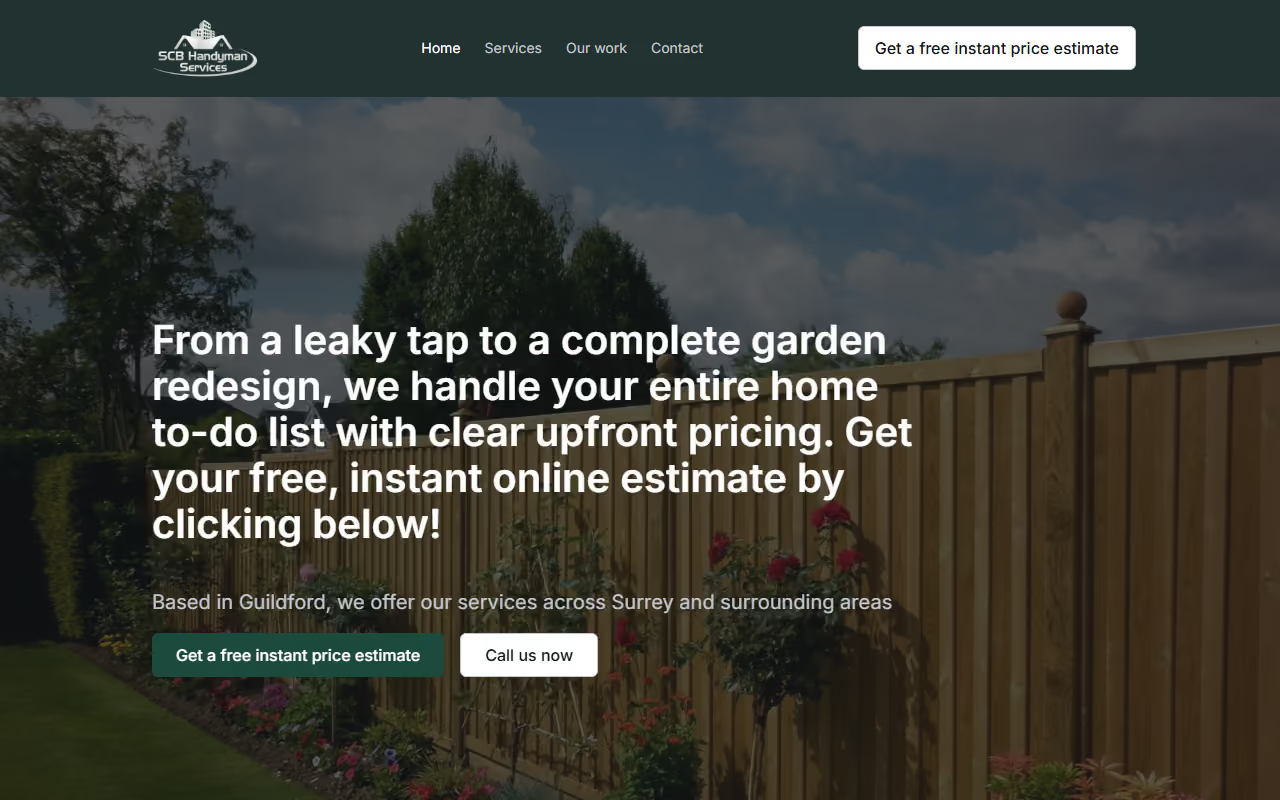
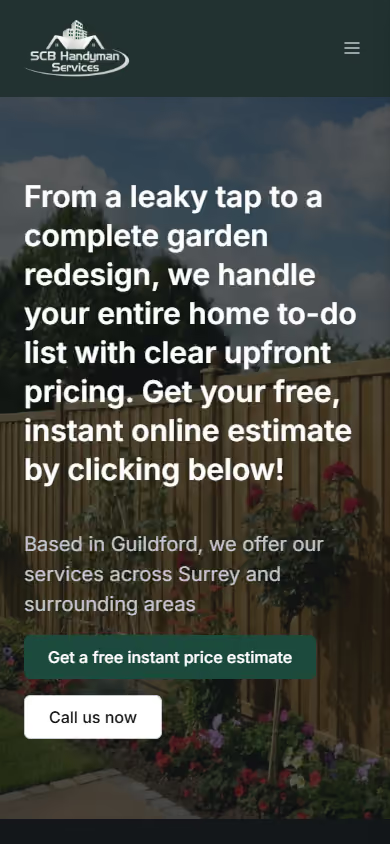
The agency works only if client results justify a monthly retainer, new clients go live quickly enough for the margin, and many small sites can be maintained without the cost growing with every client. That is why the software is one engine configured per client rather than a site built from scratch each time. SCB Handyman Services in Guildford is the first client: this is their live site, with the quote wizard I built, and the pipeline behind it.
What it does
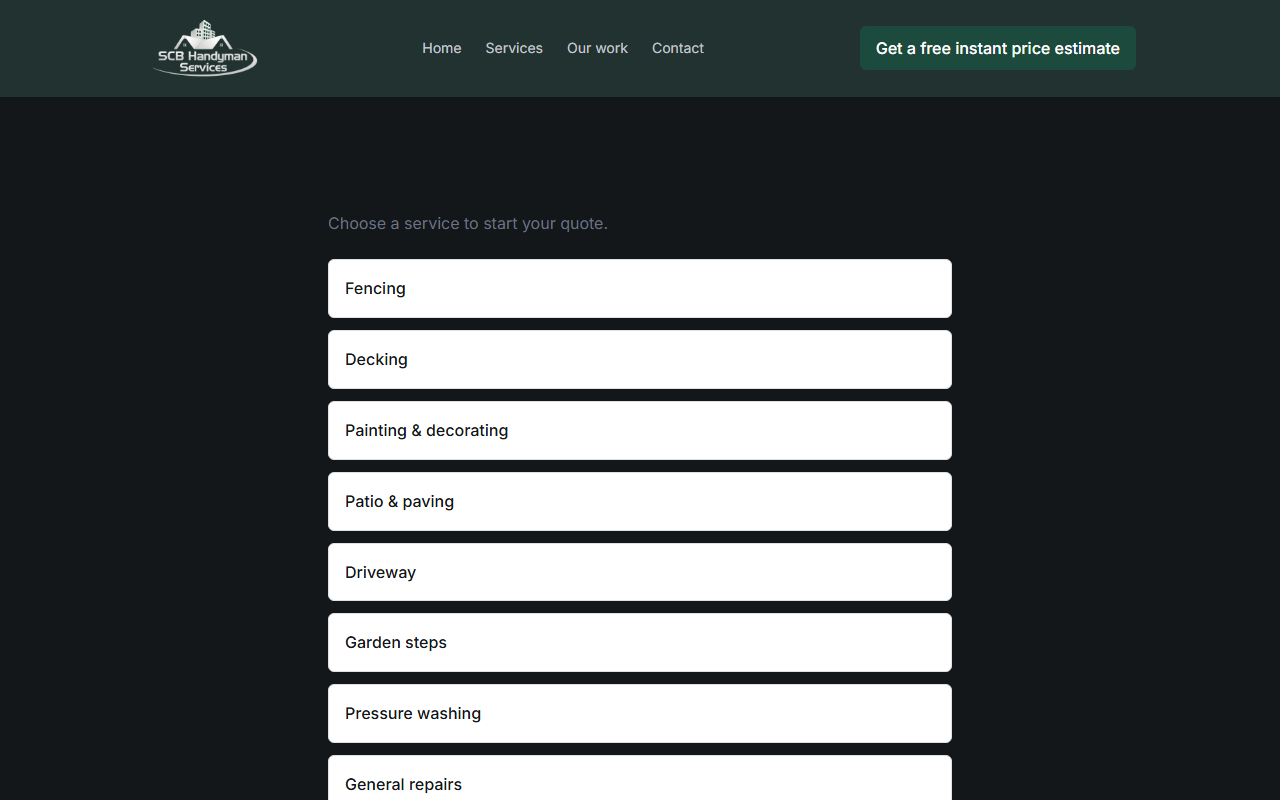
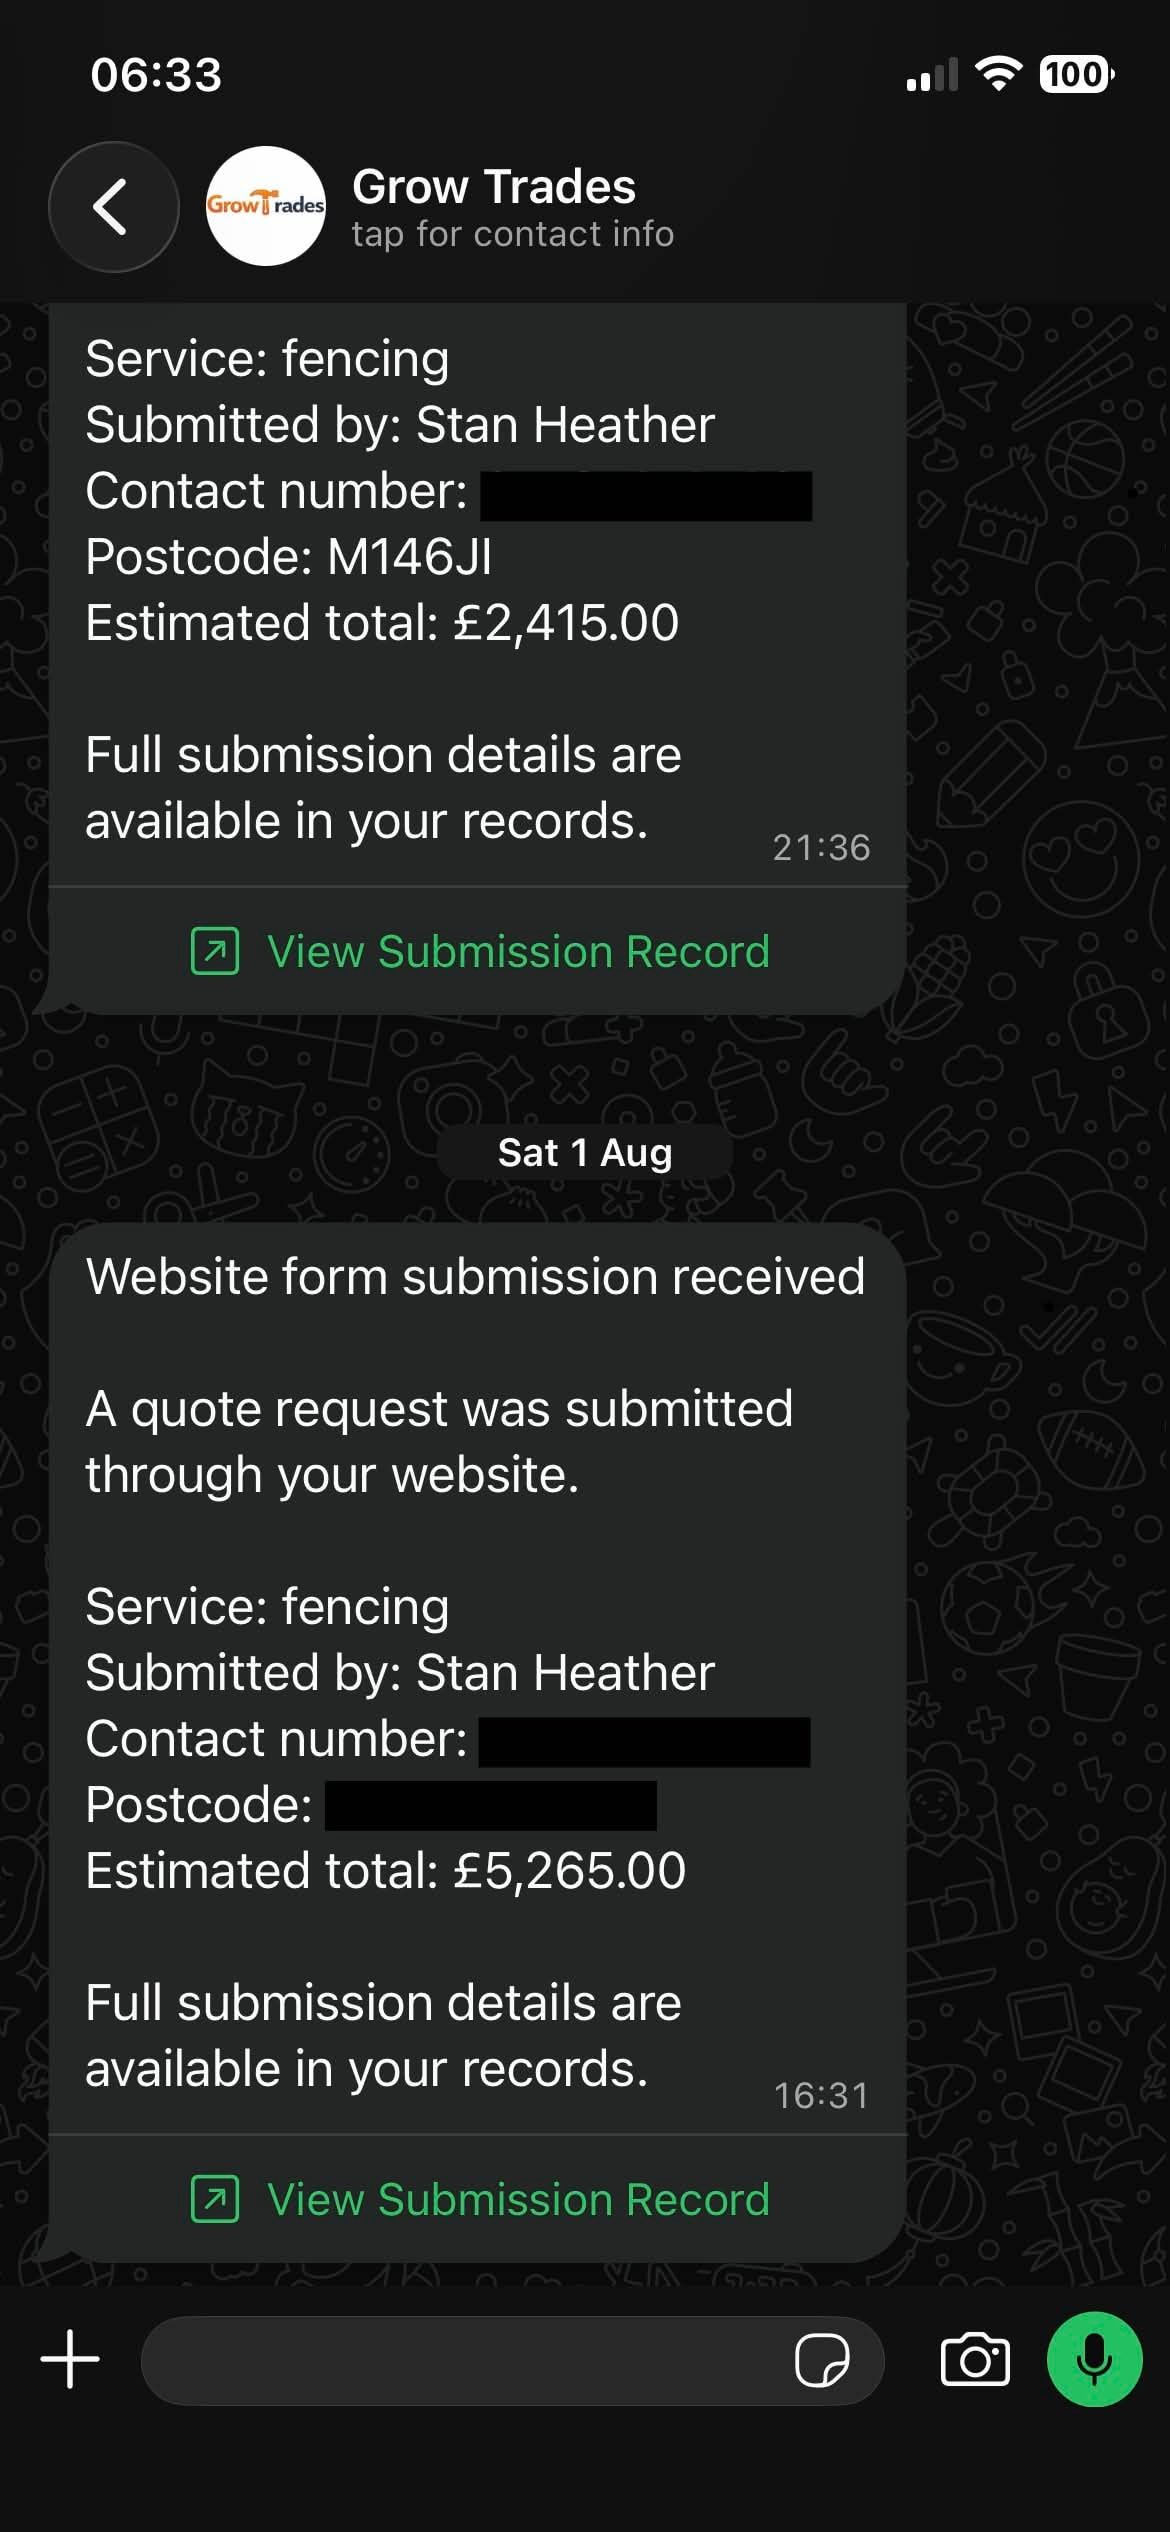
A homeowner chooses a service, answers a few questions about the job, and sees an estimated price range straight away; services that need pricing by hand send a quote request instead. Each request becomes a row in the business’s Google Sheet and a WhatsApp message to the owner.
Under the hood
The submission pipeline behind the quote form, step by step, beside the code that runs it. It began as a WordPress plugin; on this site the same pipeline runs on a Cloudflare Worker, ported with its tests.
Honeypot
A field people never see. Anything that fills it in is turned away quietly, before any other work is done.
bot-protection.tsADR-0027: Bot protection
// Layer 1: a real visitor never fills the hidden field.
if (String(payload.honeypotValue ?? '') !== '') {
  return { allowed: false, errorCode: 'honeypot_filled' };
}
Rate limit
Five messages an hour from one connection. The window keeps its original end time however many messages arrive, and the address is stored only as a keyed hash.
rate-limit.tsADR-0027: Bot protection
async record(key: string): Promise<void> {
  const entry = await this.read(key);
  if (entry === null) {
    await this.store.put(key, { count: 1, expiresAt: this.now() + this.windowSeconds });
    return;
  }
  await this.store.put(key, { count: entry.count + 1, expiresAt: entry.expiresAt });
}
Turnstile
Cloudflare's check that a person is using the form. A token only counts if it was issued for this site and this form.
turnstile.tsADR-0038: Turnstile gates both submit buttons
export function turnstileMatches(
  result: TurnstileResult,
  expected: { hostnames?: readonly string[] | undefined; action?: string | undefined },
): boolean {
  if (!result.success) return false;
  const hostnames = (expected.hostnames ?? []).filter(Boolean);
  if (hostnames.length > 0 && !hostnames.includes(result.hostname ?? '')) return false;
  if (expected.action && result.action !== expected.action) return false;
  return true;
}
Consent
Nothing is stored unless the consent box was ticked, checked on the server so a request that skips the form cannot skip it.
consent.tsADR-0029: Data protection
export function isConsentGiven(answers: Readonly<Record<string, unknown>>): boolean {
  const answer = answers[CONSENT_FIELD_KEY];
  return Array.isArray(answer) && answer.includes(CONSENT_VALUE);
}
Duplicates
A second message from the same email within 24 hours is kept and flagged, but the owner is not notified twice.
duplicates.tsADR-0028: Duplicate prevention
export async function checkDuplicate(
  repository: Pick<SubmissionRepository, 'findRecentByContact'>,
  email: string,
  phone: string,
  now: number = Date.now(),
): Promise<DuplicateCheck> {
  const emailNorm = normaliseEmail(email);
  const phoneNorm = normalisePhone(phone);
  if (emailNorm === '' && phoneNorm === '') return { isDuplicate: false };
  const windowStart = new Date(now - DUPLICATE_WINDOW_MS).toISOString();
  const match = await repository.findRecentByContact(emailNorm, phoneNorm, windowStart);
  return match === null
    ? { isDuplicate: false }
    : { isDuplicate: true, originalSubmissionId: match };
}
Persist before forward
Every enquiry is saved before anything else happens, so a failure further along can never lose a customer.
submit.tsADR-0001: A thin endpoint that persists first
let id: number;
let reference = deps.newReference();
try {
  try {
    id = await deps.repository.insert({ ...row, reference });
  } catch {
    // A reference collision is astronomically unlikely; one fresh try covers it.
    reference = deps.newReference();
    id = await deps.repository.insert({ ...row, reference });
  }
} catch (error) {
  log(`submit: persist failed (${error instanceof Error ? error.message : 'unknown'})`);
  return json(500, { errorCode: 'persistence_failed' });
}
Formula-injection sanitising
The copy that goes to the spreadsheet is cleaned: markup removed, and anything a spreadsheet would run as a formula made inert. The stored original is untouched.
sanitize.tsADR-0037: Security posture
function sanitizeText(value: string): string {
  let text = value.replace(/\0/g, '');
  text = text.replace(/<(script|style)[^>]*?>[\s\S]*?<\/\1>/gi, '');
  // Tags, including one left unclosed at the end; a lone "<" in "x < y" stays.
  text = text.replace(/<\/?[a-z!][^>]*(>|$)/gi, '');
  text = text.replace(/[\r\n\t ]+/g, ' ').trim();
  if (text !== '' && FORMULA_TRIGGERS.has(text.charAt(0))) text = `'${text}`;
  return text;
}
Forward
The enquiry goes to the automation that writes the spreadsheet row and notifies the owner, signed with a shared secret. A failure is retried later.
forwarder.tsADR-0043: The pipeline on the Worker
export async function forward(
  input: ForwardInput,
  webhook: WebhookConfig,
  fetchImpl: typeof fetch = fetch,
): Promise<ForwardResult> {
  if (!webhook.url) return { ok: false, error: 'webhook_not_configured' };
  const headers: Record<string, string> = { 'Content-Type': 'application/json' };
  if (webhook.secret) headers['X-Webhook-Secret'] = webhook.secret;
  try {
    const response = await fetchImpl(webhook.url, {
      method: 'POST',
      headers,
      body: JSON.stringify(webhookPayload(input)),
      signal: AbortSignal.timeout(TIMEOUT_MS),
    });
    if (response.status < 200 || response.status >= 300) {
      return { ok: false, error: `http_status_${response.status}` };
    }
    return { ok: true };
  } catch (error) {
    return {
      ok: false,
      error: `transport_error: ${error instanceof Error ? error.name : 'unknown'}`,
    };
  }
}
Retention
Enquiries are deleted after 90 days, and rate-limit records as soon as their hour is over.
scheduled.tsADR-0043: The pipeline on the Worker
export async function pruneExpired(deps: {
  repository: Pick<SubmissionRepository, 'deleteOlderThan'>;
  deleteExpiredRateLimits: (nowSeconds: number) => Promise<number>;
  retentionDays: number;
  now?: () => number;
}): Promise<{ submissions: number; rateLimits: number }> {
  const now = (deps.now ?? Date.now)();
  const cutoff = new Date(now - deps.retentionDays * DAY_MS).toISOString();
  return {
    submissions: await deps.repository.deleteOlderThan(cutoff),
    rateLimits: await deps.deleteExpiredRateLimits(Math.floor(now / 1000)),
  };
}
Engineering
Authorship
My role: founder.